Clause 7.8 — Product cybersecurity monitoring and issue management
Subclause 7.8 specifies requirements for monitoring the threat landscape, handling discovered vulnerabilities, and managing security incidents under FprEN 40000-1-2:2026.
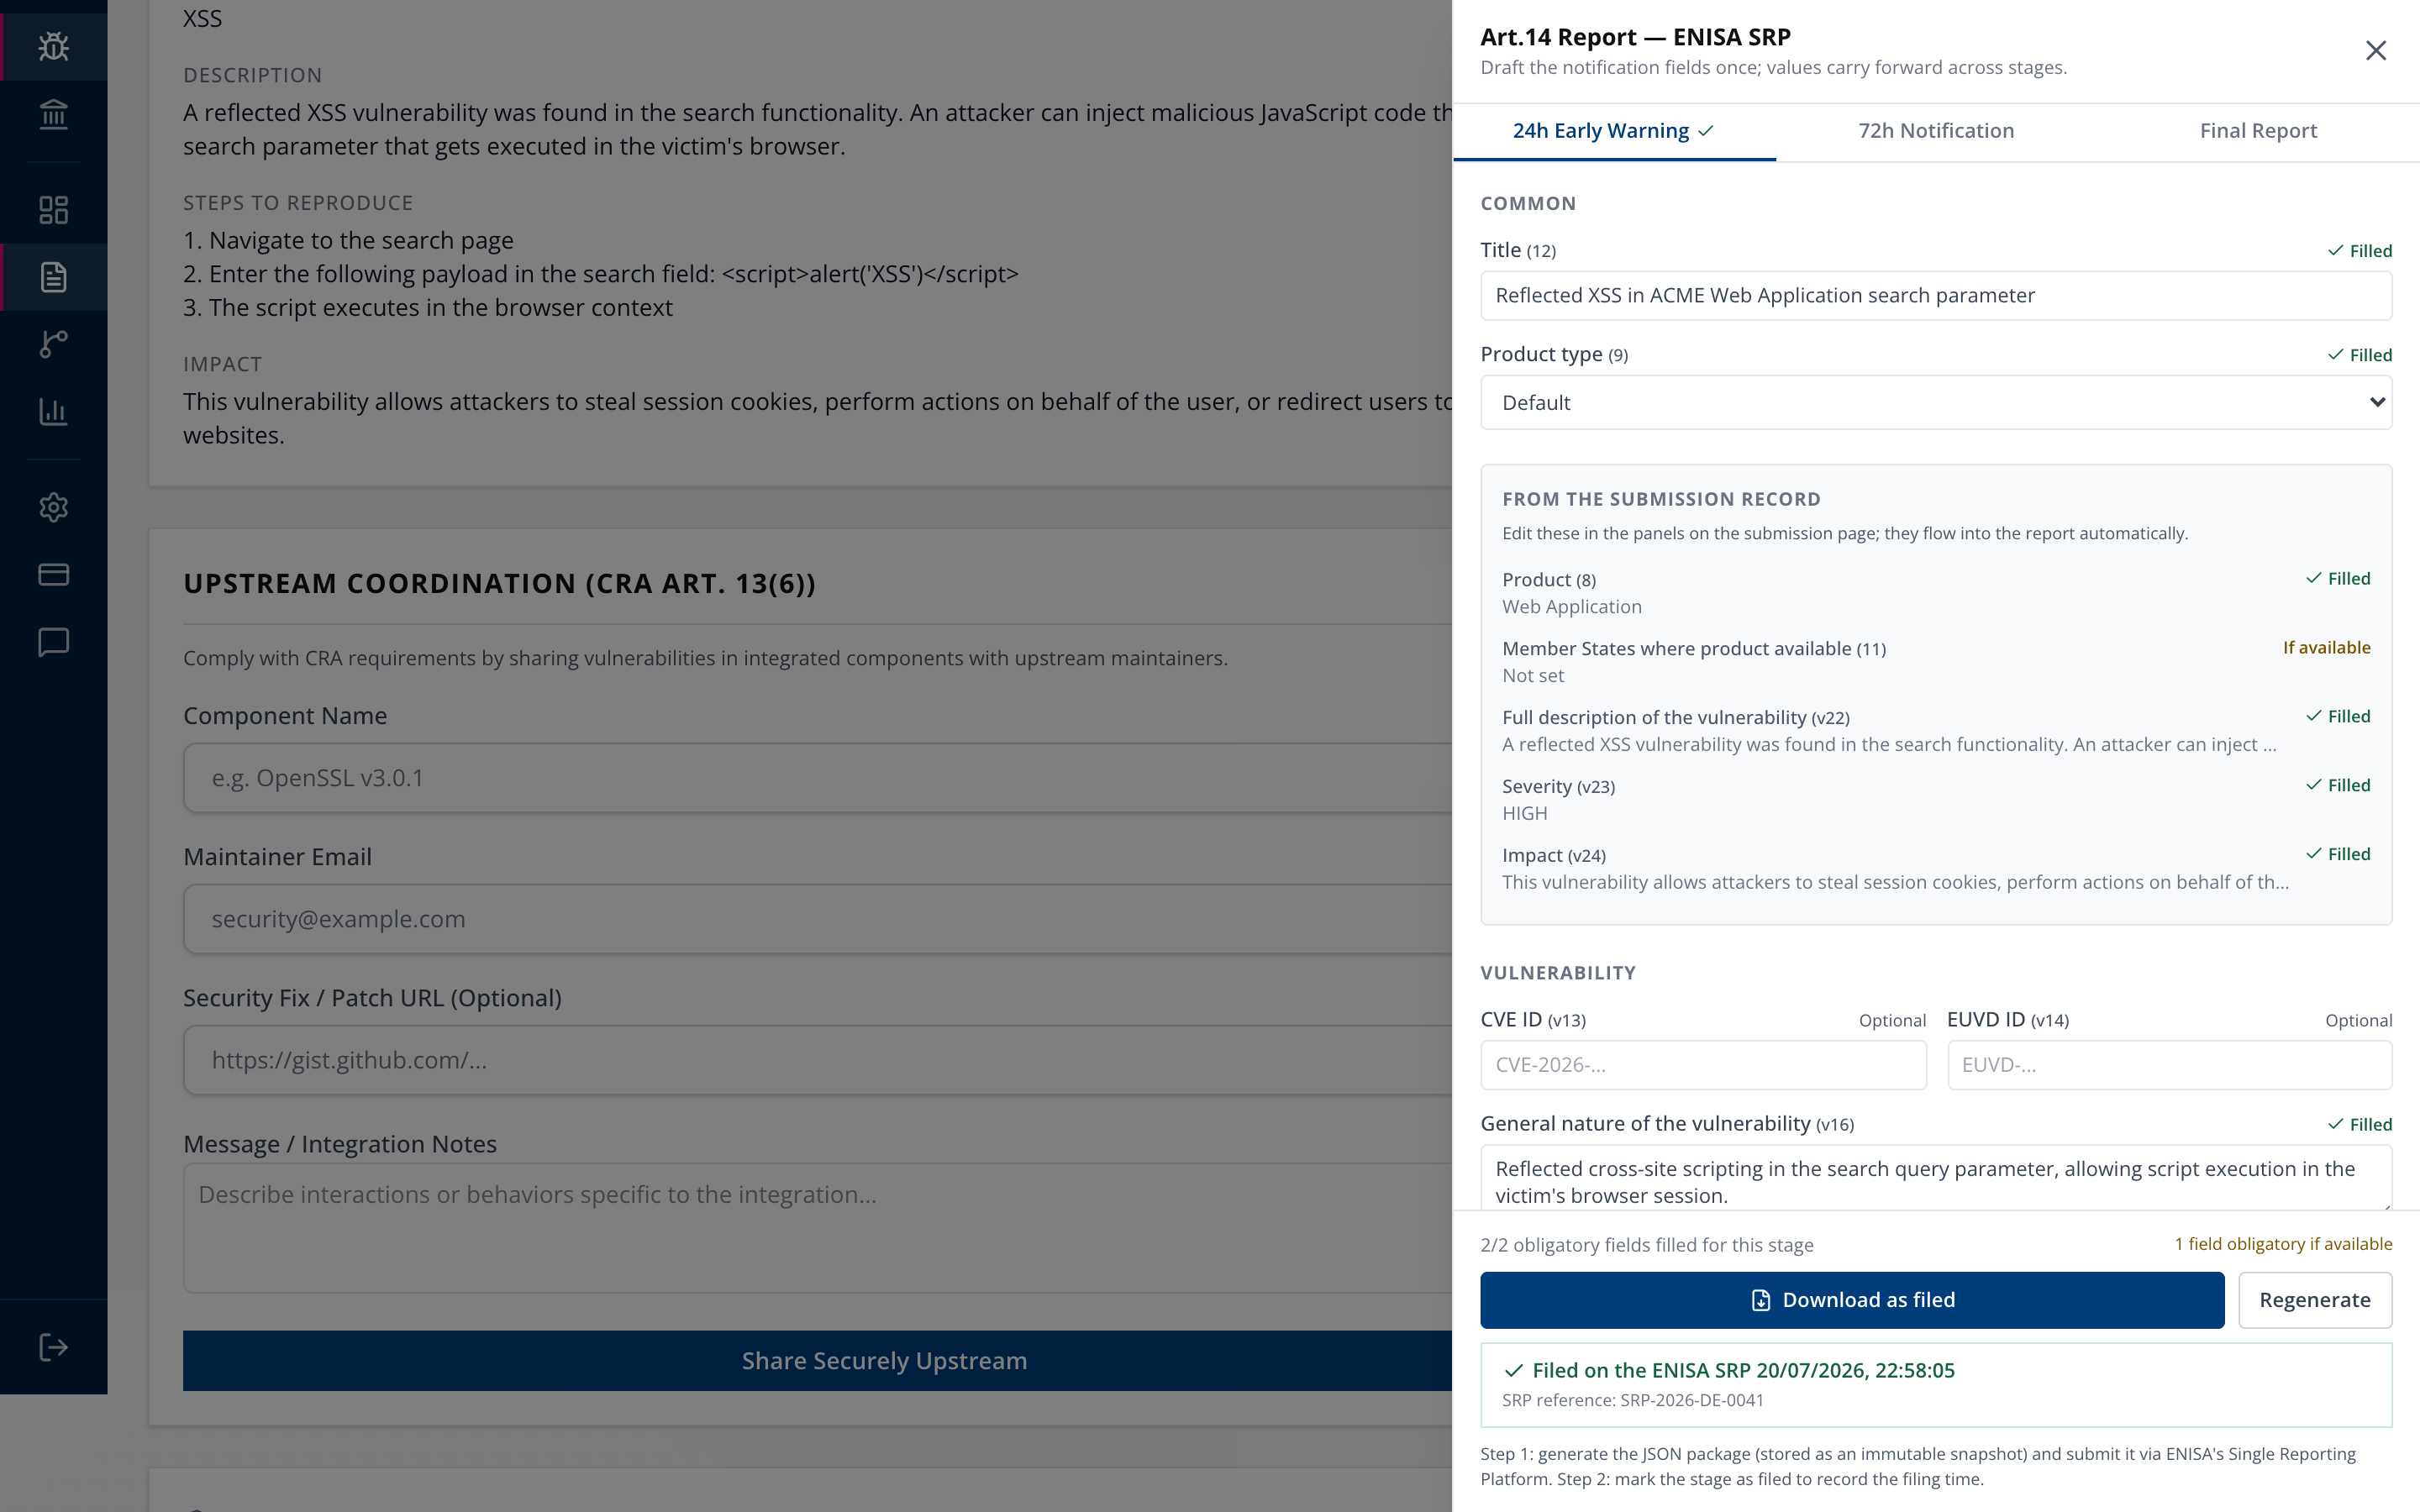
Portal UI Path: Vulnerability disclosure → Submissions → [Select Report] → Art.14 Report
Related Procedures:
What Clause 7.8 requires
Requirements
[CLA-08-RQ-01]: Manufacturers shall monitor and react to changes in product risk assessments (6.4), incidents, and vulnerabilities at justifiable periodic intervals.[CLA-08-RQ-02]: Discovered vulnerabilities shall be addressed in line with risk assessment (6.4) and risk communication (6.6) (aligned with prEN 40000-1-3).[CLA-08-RQ-03]: Verified cybersecurity incidents shall be addressed without undue delay.[CLA-08-RQ-04]: Residual risks resulting from incidents shall be communicated in alignment with 6.6.
How CVD Portal supports compliance
CVD Portal provides a comprehensive vulnerability intake, monitoring, and reporting platform:
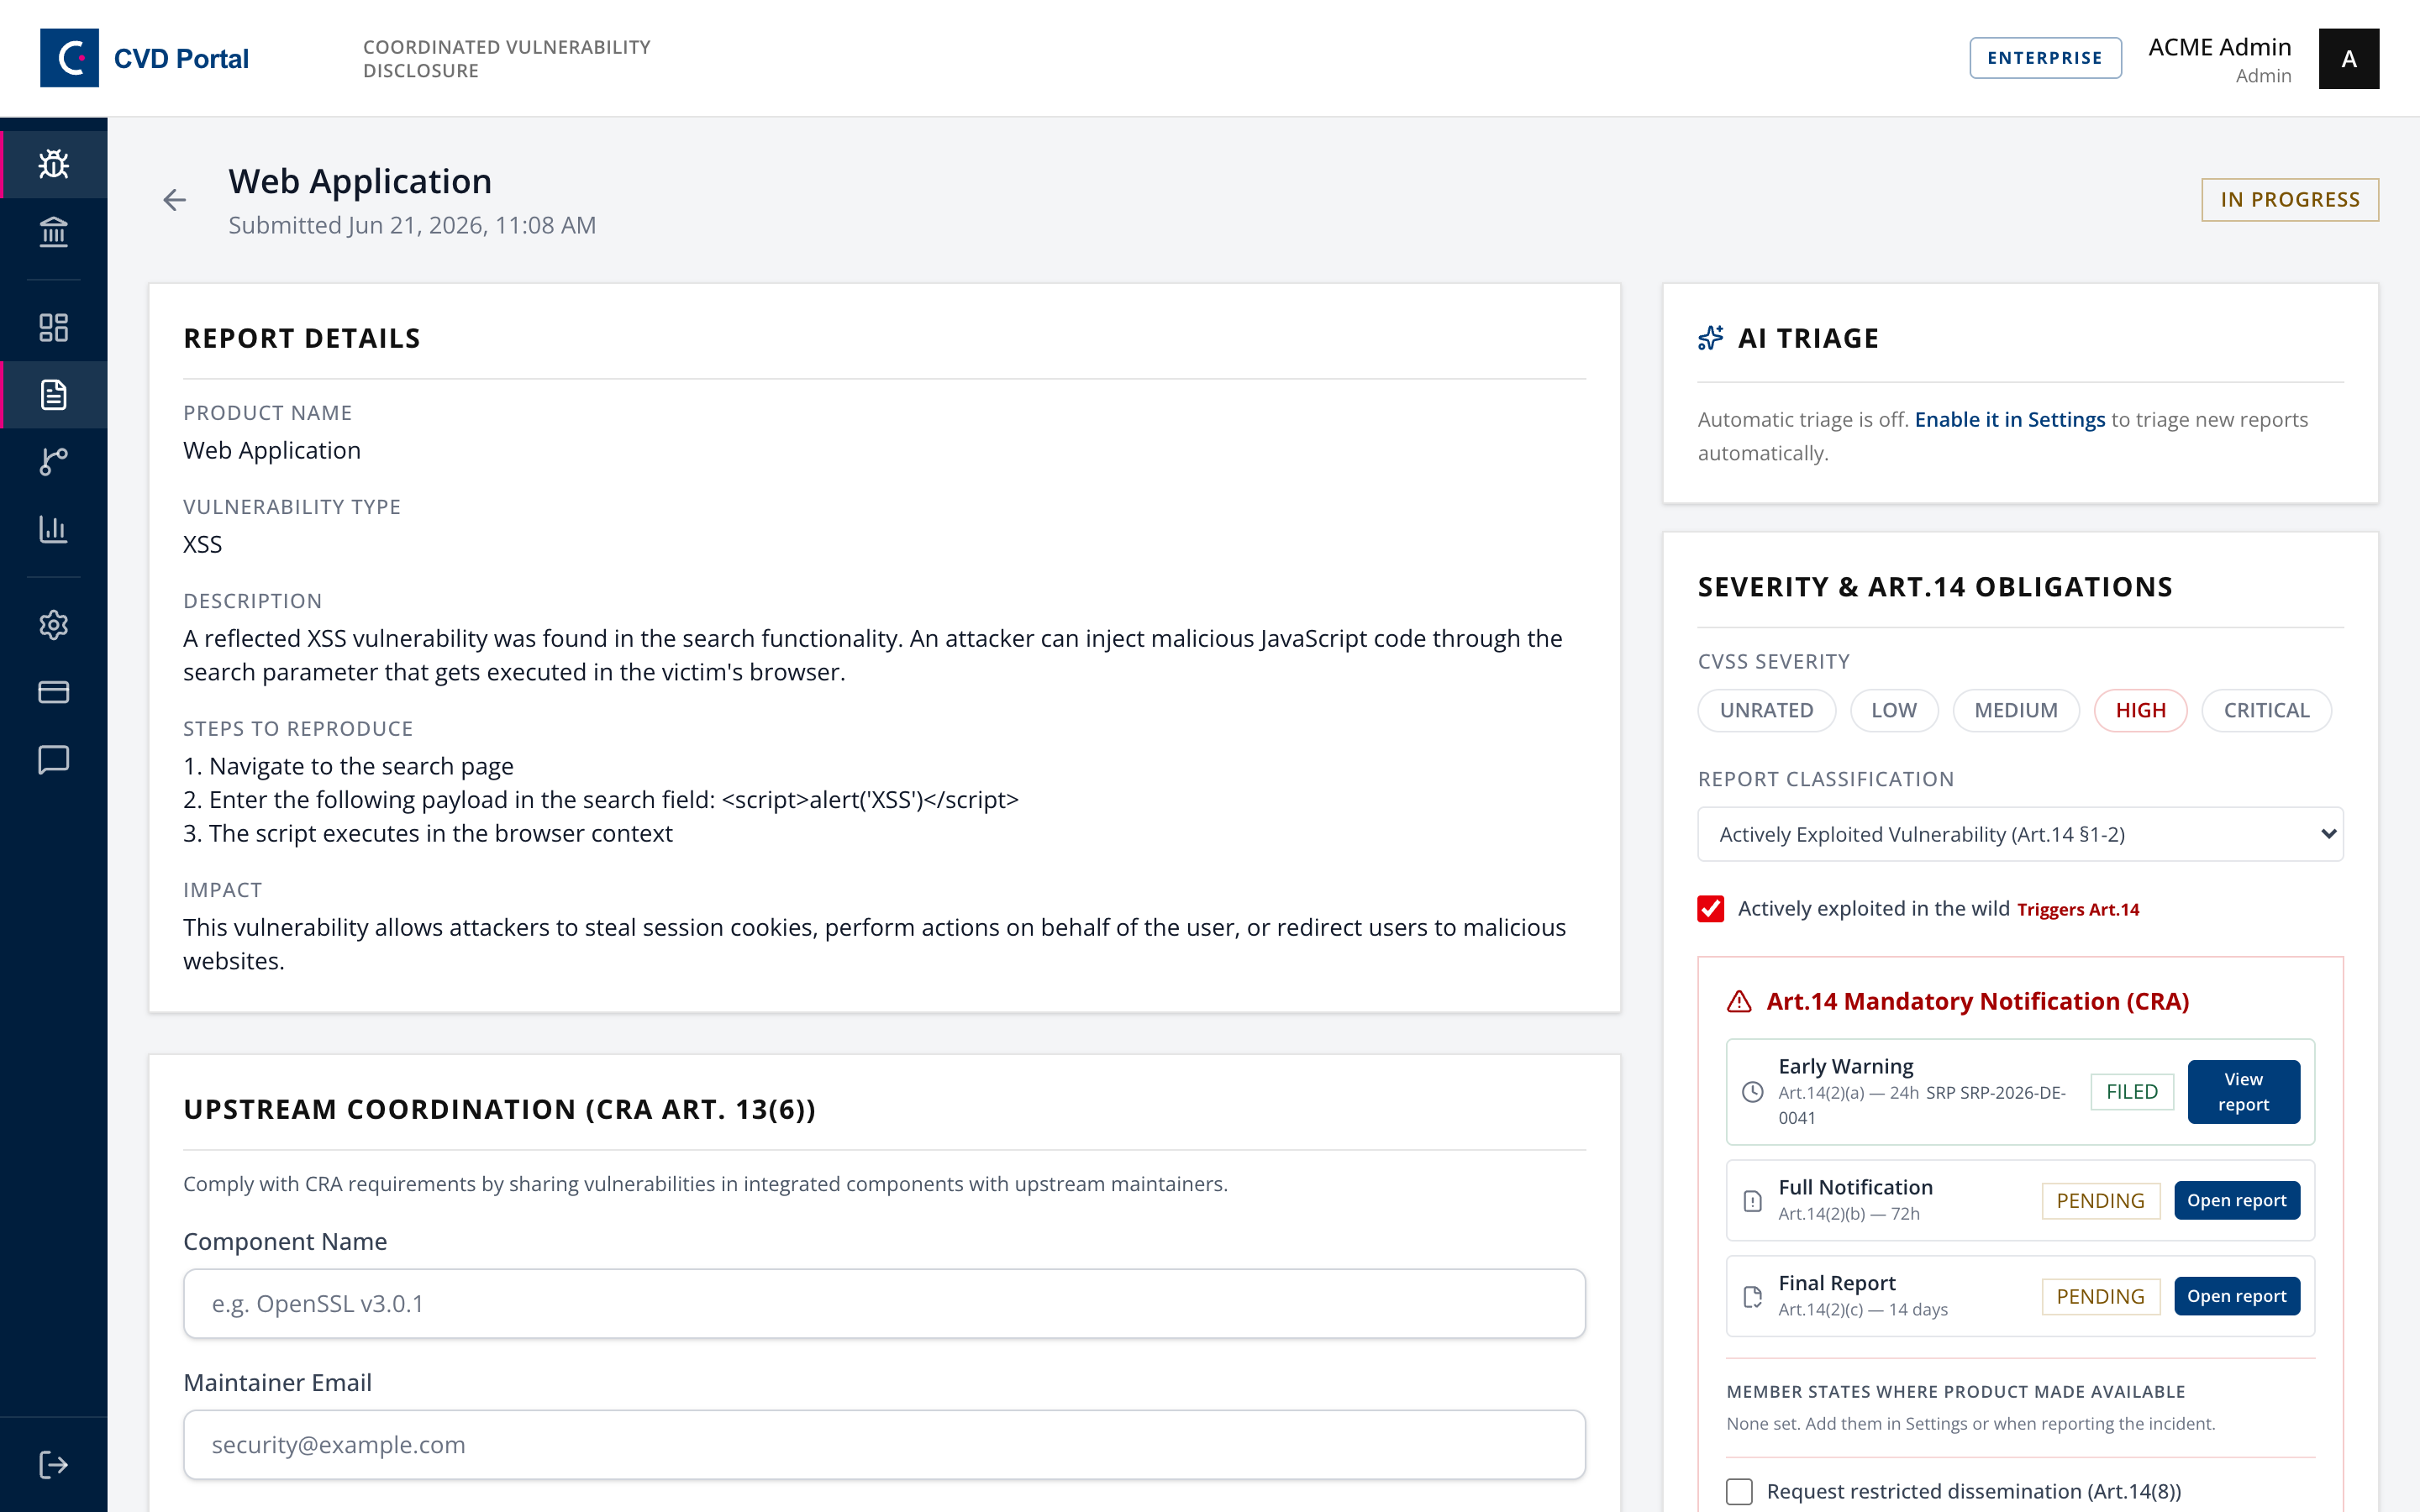
- Coordinated Vulnerability Disclosure (CVD) Portal: Provides a dedicated, whitelabel intake form (
acme.cvdportal.com) with a published PGP key, encryption of report fields at rest, and acknowledgment SLA tracking. - Automated threat monitoring: Matches uploaded SBOMs against OSV advisories and checks findings for exploitation in CISA KEV and GCVE sources. On the Enterprise plan, a daily job rescans every SBOM and alerts on new findings.
- Article 14 early warning & incident engine: Automated deadline banners guide you through mandatory 24-hour early warnings, 72-hour notifications, and final reports to ENISA and CSIRTs.
- CSAF 2.0 advisory publisher: Generates machine-readable CSAF 2.0 advisories and Article 14(8) user advisories in CSAF VEX format on request.